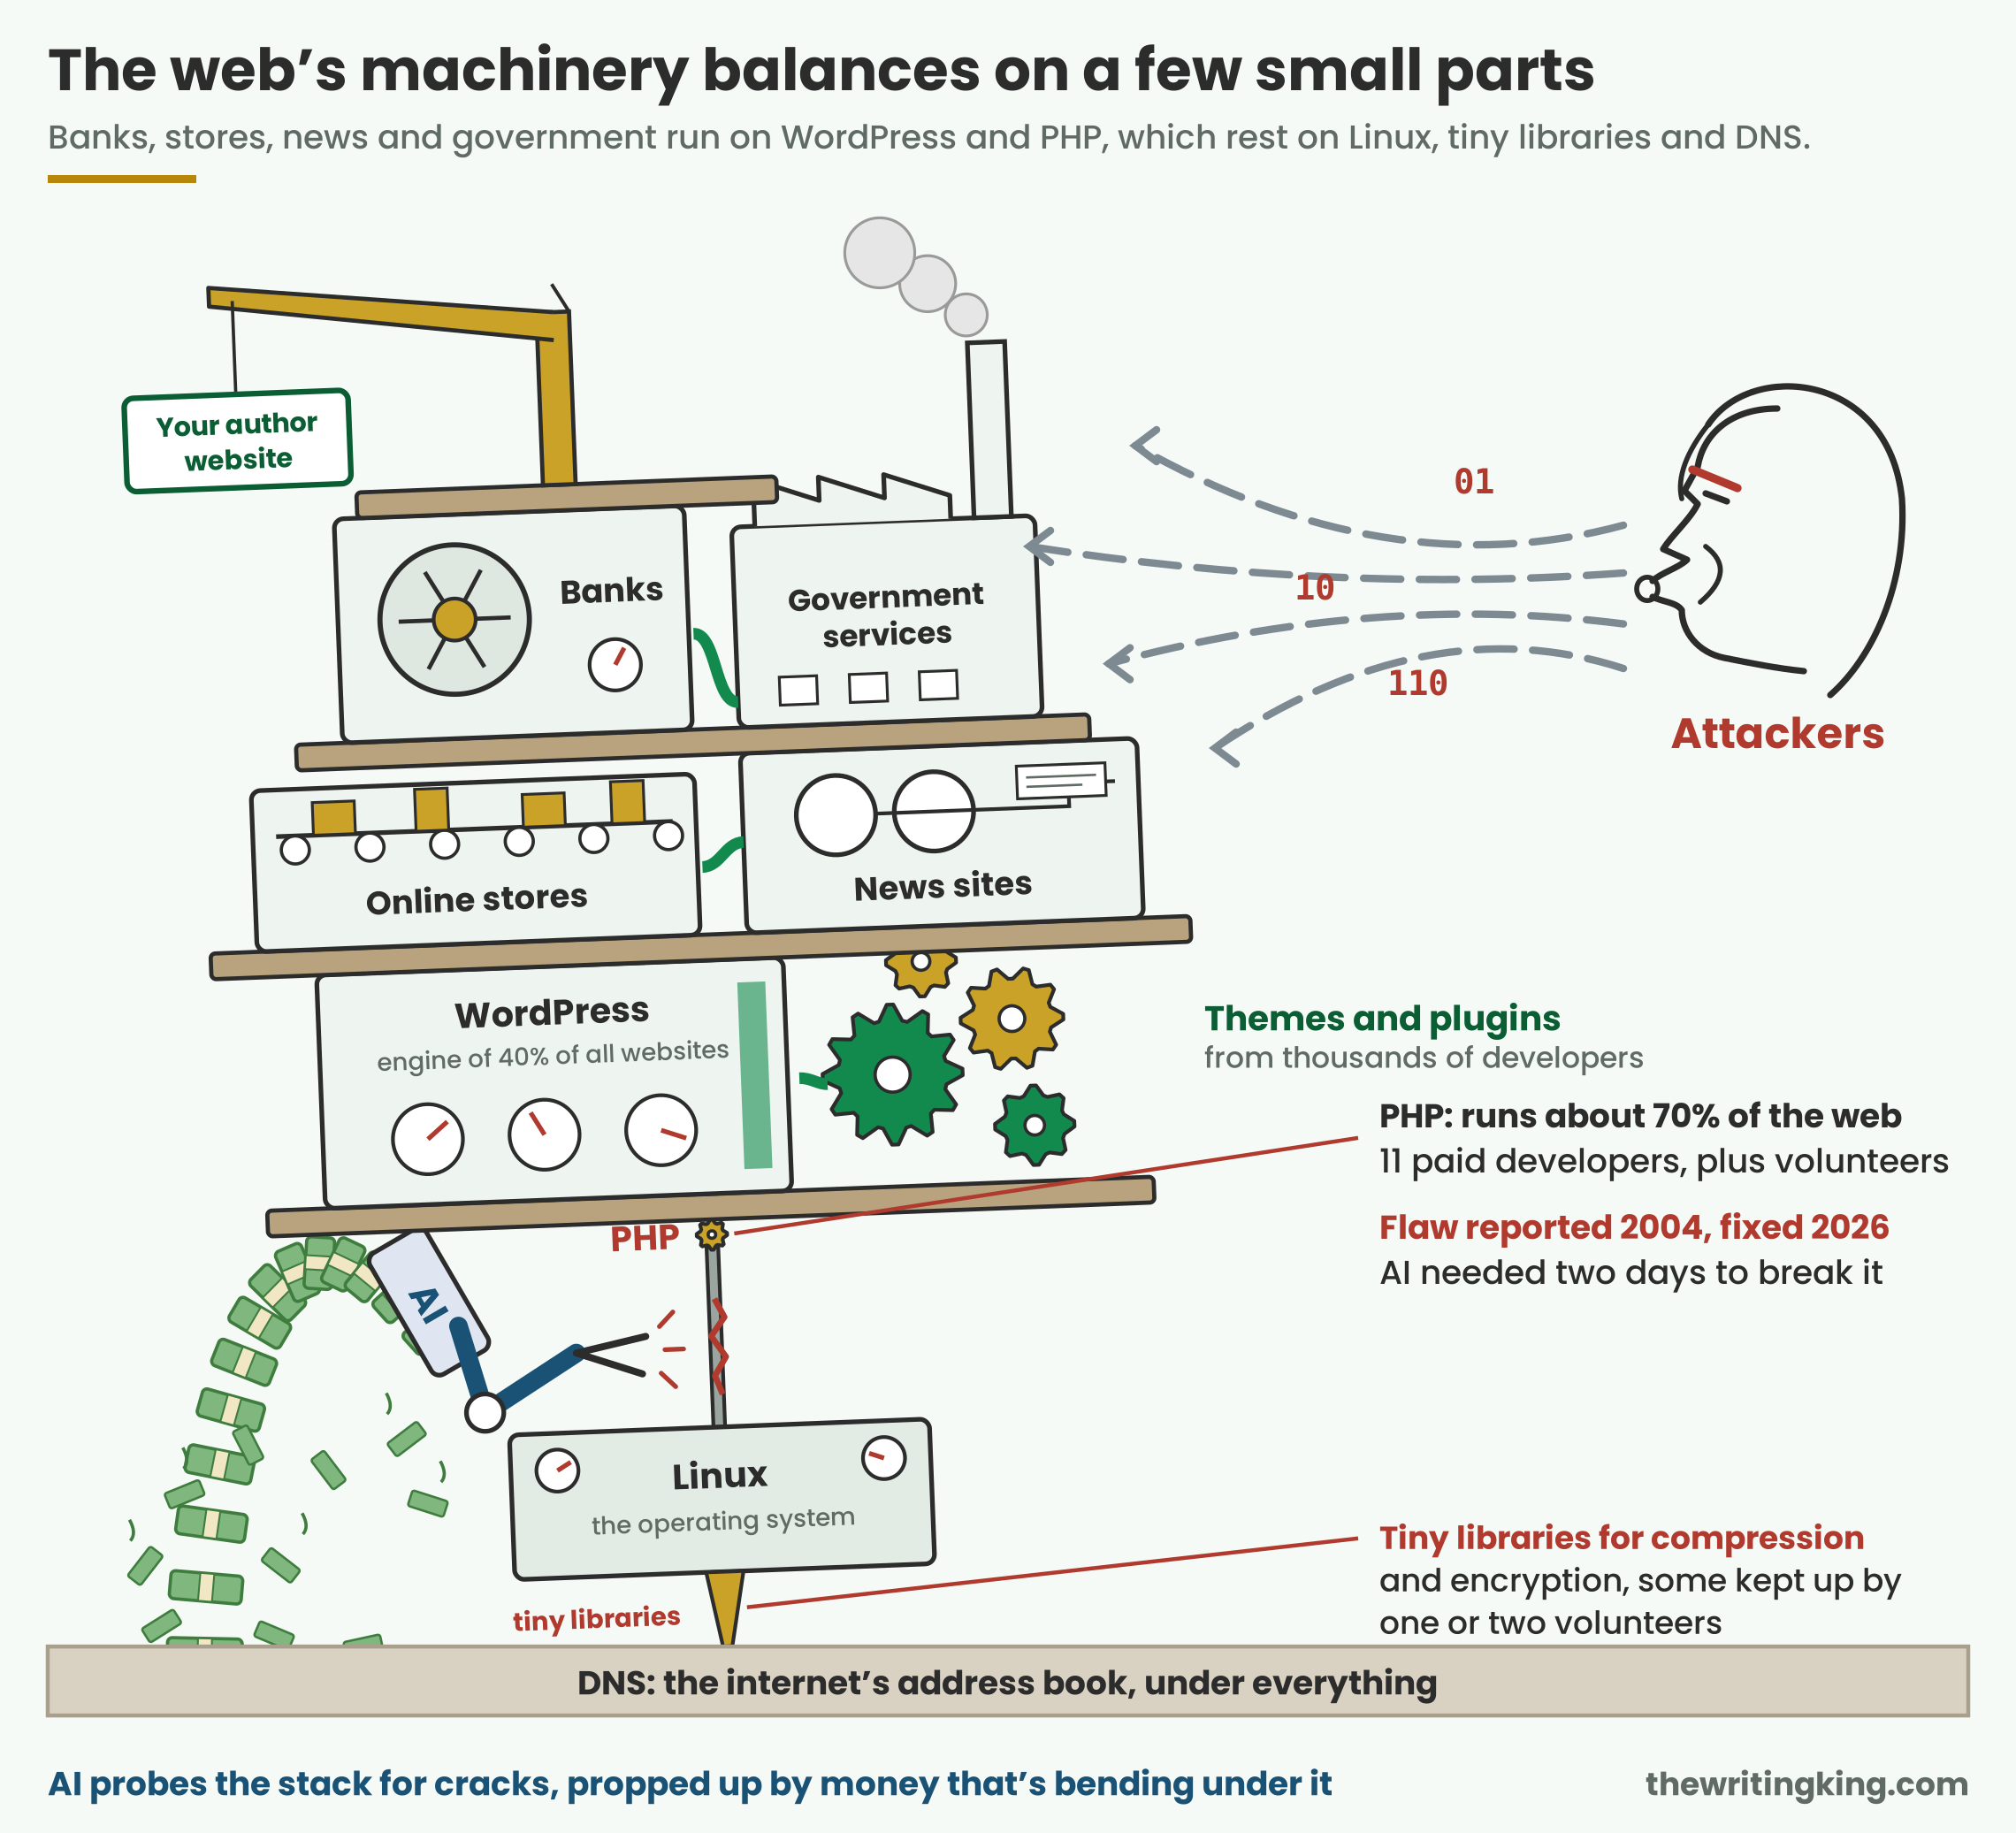
Picture the web as a tower of machines. Banks, online stores, news sites and government services sit on top. Under them run WordPress, themes and plugins. Under those turns PHP, one small gear kept going by a few people. And off to the side stands AI, propped up on a towering pile of money, poking at that small gear to see where it cracks.
This week it found a crack. An AI model broke a PHP flaw that had sat there since 2004, and the patch shipped on October 21 with attackers already on its heels. I wrote about what PHP2Shell means for your website. The money side deserves its own look.
My position is simple. The AI companies should pay to support and improve PHP. They have the money, they profit from the web PHP runs, and their own tools just made the maintainers’ job a lot harder.
Banks, stores, news sites and government services run on WordPress and PHP. Below those sit Linux, a few tiny libraries kept up by volunteers, and DNS. AI probes for cracks from one side, propped up by money that's bending under it, while attackers blow on the other.
How much money goes into AI compared with PHP?
It’s a gap that’s hard to take in. Amazon, Microsoft, Alphabet and Meta told investors this spring they plan about $725 billion in capital spending for 2026, most of it for AI and the data centers that run it. That’s up 77% from a record $410 billion the year before.
The PHP Foundation’s 2025 report lists $730,534 in donations for the whole year. It paid 11 developers to work on PHP going into 2026. It spent about $139,000 more than it took in, on purpose, because the work needed doing.
Put those side by side and the four companies plan to spend close to a million dollars on AI for every dollar PHP’s foundation received. PHP isn’t a hobby project, either. It runs about 70% of the websites that use a server-side language, including every WordPress site, mine among them.
| Item | Amount | Source |
|---|---|---|
| Planned 2026 capital spending, Amazon, Microsoft, Alphabet and Meta | About $725 billion | Company guidance, reported April 2026 |
| OpenAI’s subsidy for defenders to use its own security models | $1 billion in access | Reported October 2026 |
| PHP Foundation donations, all of 2025 | $730,534 | PHP Foundation 2025 report |
| Developers the PHP Foundation pays | 11 | PHP Foundation 2025 report |
| OpenSSL donations before Heartbleed | About $2,000 a year | Reported April 2014 |
Why should AI companies pay to support PHP?
A flaw is cheap to find now. A fix still isn’t.
Three reasons, and any one of them would be enough.
They profit from it. AI coding tools learned to write code from enormous amounts of public, open-source code, and a lot of that code is PHP. The web pages, stores and businesses that pay for AI products run on it. Nobody at these companies built PHP, and all of them benefit from it every day.
Their tools changed the job. For 22 years the PHP flaw sat there because exploiting it was too tedious for any human attacker. AI ended that. The same tools that found it can find the next one, and the one after that. A flaw is cheap to find now. A fix still isn’t. The PHP2Shell fix took a major change to the PHP engine and coordination among the maintainers, and those maintainers are the same 11 paid developers plus volunteers.
The money is already there. PHP’s whole annual budget, paid several times over, would be a rounding error for any one of these companies. One senior AI researcher’s pay package can be bigger than the PHP Foundation’s year.
I don’t think any of this is charity. A company that sends a flood of bug reports into a project run by a dozen people and offers nothing else is handing them work. A company that funds the people who fix what its tools find is protecting the platform its own customers stand on.
AI companies plan to spend about $725 billion this year. PHP, which runs 70% of the web, got about $730,000. They should pay to keep it alive.Share on X
What other old technology is the web still balanced on?
My drawing shows a handful of small parts. The real picture has thousands, and plenty of them are older than PHP.
COBOL is the obvious one. It dates to 1959, and it still runs a huge share of the world’s banking. Reuters reported in 2017 that about 220 billion lines of COBOL were still in use, handling 95% of ATM swipes and 80% of in-person card transactions. When unemployment claims flooded in during the spring of 2020, New Jersey’s governor went on television asking for volunteers who knew COBOL, because the state’s benefits system ran on it and the people who understood it had retired.
Time is another. Nearly every computer on the internet sets its clock with NTP, the Network Time Protocol. In 2015 the reference software for it was being kept alive mostly by one man, working part time on very little money. The time zone database that tells your phone when daylight saving starts is maintained by a small group of volunteers.
Then there’s routing. BGP, the protocol that decides how traffic moves between the networks that make up the internet, was designed in 1989. In 2021 a botched configuration change pulled Facebook’s BGP routes off the internet and took Facebook, Instagram and WhatsApp offline for about six hours.
None of these are glamorous. All of them are gears in the tower, and AI can probe every one of them. Money for PHP would be a start. The same companies should be looking at the rest of the list.
Isn’t open-source software supposed to be free?
Free to use, yes. That’s the deal, and it’s a good one. Nobody has to ask permission or pay a license fee to build on PHP. That freedom is a big reason the web grew the way it did.
But free to use was never free to maintain. Somebody still reviews every change, fixes every flaw and tests every release. For PHP that’s a foundation running a deficit and volunteers working nights. The license doesn’t require anyone to pay. Plain sense says the companies taking the most out should put some back.
Would you run a business in a building whose entire maintenance crew was 11 people and a tip jar? Most of the web does.
Why does PHP funding matter to an author with a WordPress site?
Because your site is sitting on that gear. Mine is. My business runs on WordPress with PHP 8.4 underneath, behind Cloudflare, with about 70 plugins I built myself. Every one of those plugins assumes PHP’s engine does what it promises. If the people who maintain PHP burn out or fall behind, I don’t get a vote. Neither do you.
Thirty-three years in technology taught me to look at what a system depends on before I trust it. For most author websites the list is short: a host, WordPress, a theme, some plugins and PHP. The first four have business models, and the last one runs on donations.
That should bother you.
Has big tech paid for open-source security before?
Once, after a disaster. In 2014 the Heartbleed bug in OpenSSL exposed encryption keys and passwords on a huge share of secure websites. Then it came out that OpenSSL, software the whole industry depended on, was run by a small crew living on about $2,000 a year in donations.
Within weeks a dozen companies, including Amazon, Cisco, Facebook, Google, IBM, Intel and Microsoft, each pledged $300,000 to a new Core Infrastructure Initiative to fund critical open-source projects. It helped. It also proved the pattern: the money shows up after the house is on fire.
Ten years later a volunteer maintaining a compression tool called xz Utils, worn out and short on help, handed commit access to a stranger who’d spent two years earning his trust. I wrote about the xz backdoor that nearly made it into Linux as a result. Same pattern, different project. Nobody pays until something breaks, and by then it’s late.
Isn’t AI finding the bugs help enough?
It’s help, and OpenAI deserves credit for it. OpenAI’s Patch the Planet coalition found the PHP flaws, worked with the PHP Foundation on the fix, and warned governments ahead of time. That’s better than an attacker finding them first.
But a bug report isn’t a salary. OpenAI’s biggest number this fall was a $1 billion program giving defenders subsidized access to its own security models. Credits for your own product are a sales channel with a good cause attached. What PHP needs is paid people, for years, doing the slow work of reviewing code, rewriting fragile parts of the engine and testing fixes across millions of servers.
There’s a mismatch building, too. If AI can find a dozen serious flaws in a weekend and the project can fix two a month, the backlog becomes the danger. Every known but unfixed flaw is a door somebody else’s AI can find. The companies building the flaw finders should be paying for the flaw fixers.
What would real AI company support for PHP look like?
More of the people who already do the work, for one. The PHP Foundation already knows how to hire and manage developers. Steady, multi-year funding lets it hire more of them and keep them, instead of running a deficit to get through the year.
Beyond that: security audits of the oldest, most fragile parts of the engine. Paid time for maintainers to handle the flood of AI-found reports. And when an AI company’s tool finds a flaw, money for the fix should come with the report. If the tool can find it in two days, the company can fund the two months it takes to fix it properly.
None of this needs a new law or a new bureaucracy. It needs the companies that profit most from the web to treat its foundation as their problem. PHP is my example because it’s the gear in the news, but the same goes for Linux, the tiny libraries under it, and the volunteers keeping them alive.
My take
The AI companies should pay to support and improve PHP. They learned from it, they profit from the web it runs, and their tools just turned 22-year-old flaws into two-day jobs. A million dollars of AI spending for every dollar PHP gets is a choice somebody made. Steady money now costs them almost nothing. The next disaster costs everybody.
What website owners can do while the big companies decide
You can’t make a trillion-dollar company write a check. You can stop pretending the software under your site maintains itself.
Look at what your site depends on and who keeps it alive. I wrote about the single maintainer problem for exactly this reason: one tired developer is a risk no feature list shows you. If a plugin or theme you rely on takes donations, send a few dollars. The PHP Foundation takes donations too. Then keep your own stack patched, because the gap between a fix and an attack is now measured in hours. For the security side, read why the supply chain is the attack surface.
The Cybersecurity Hub collects my security articles, and if you want help keeping an author site patched and lean, my WordPress service is the place to start. The tower of machines will keep getting taller. Somebody has to pay for the gear at the bottom, and the people with the biggest pile of money are standing right next to it.

I wrote this about the choices big platforms made for profit, one sin per chapter, greed included, with a section on what to demand and from whom.