Latest
SMS Appointment RemindersDarrell Stern: Stop Being Invisible, Become UnmissableFree BooksJoe Rockey: Ghostwriting His BookHow to Turn Your Expertise Into a Book People Want to Read | The Expert MethodWhat’s New at The Writing King: Week of October 25, 2026Challenger Remembrance Day: The Engineer Who Wouldn’t SignJoel Salomon: The Truth About MoneyReddit Is Putting Up a Login Wall. Wikipedia Won’t Be Far Behind.Victoria Chemko: The Body Is the First TechnologySir Patrick Stewart: A TributeA Year in the Bank: ADHD, Face Blindness and the Freedom to Walk Out | The Impossible Puzzles Show, Episode 326A Yale Economist Says We Won’t Be Missed. He Forgot the Bread Line.Walter Koenig: A TributeAI Has Paid Off Outside Tech. Apollo Is Reading the Wrong Scoreboard.I Don’t Post Bad ARC Reviews. I Send the Author a Note.The Little Red Book of Stuff That Works!Your Kids Are Your Own FaultGrow a PairYou’re Broke Because You Want to BeIt’s Called Work for a Reason!No Time for TactShut Up, Stop Whining, and Get a LifeWilliam Bessette: AI Enablement and Child Welfare TechnologyFree Book Planning ToolsWhat’s New at The Writing King: Week of October 18, 2026Ghostwriting by the Numbers: Timelines, Word Counts and the First CallPromising Young Woman (2020) ReviewBillions for AI, Pennies for the Plumbing: AI Companies Should Pay to Keep PHP AlivePHP2Shell: AI Found a 22-Year-Old Crack Under Your Website in Two DaysPetrov Day: The Officer Who Didn’t Believe the ComputerKindle Unlimited Is Now Kindle+. AI Audiobooks Just Joined the BuffetMo Gawdat Says the AI Dystopia Starts in 2027. Read the List, Skip the DatesChina Is Using Bots to Fan the Data Center Backlash. The Backlash Is Still Real.The Society of Authors Signed an Ethical AI Charter, Then Ran From It in Eight DaysWhen to Quit Writing a Book: I’ve Abandoned Dozens, and I’d Do It AgainGetty Images Filed for Bankruptcy. Can You Prove You Licensed Your Book’s Images?Fluff Words: Cut Them From Your Prose, Keep Them in Your DialogueWhere Can Writers Learn Storytelling From Movies? Richard Lowe Publishes 1,226 Film and TV Reviews With Writing Craft NotesWhere Are the Independent Bookstores and Public Libraries Worth Visiting in Tampa Bay? Author Richard Lowe Profiles 44 of ThemWhat Should You Know Before Hiring a Ghostwriter? The Writing King Publishes 57 New Answers, Including What to Do When It Goes WrongWhere Can You Hear Founders and Executives Tell Their Own Stories? Richard Lowe’s Leaders and Their Stories Publishes Every Unscripted Interview With a Full TranscriptAuthor Richard Lowe Publishes Eight Volumes of Enemies of You, a Researched Series on the Forces Working Against Ordinary AmericansThe Jackal (1997) ReviewThe Day of the Jackal (2024) ReviewYour First Novel Is an Apprentice Piece: What Beta Readers and Editors Can’t FixWhen the Cloud Gets Bombed: What the AWS Data Center Strikes Teach About BackupsHuman-Written Book Labels Are Gatekeeping With a FeeThe Enshittification of Microsoft Office: Why I Switched to a Free CloneGlobal Encryption Day: The Padlock Every Writer Depends On
The Writing King Your Ethical Ghostwriter. Your Story, Done Right.

The Fake Printer Guy: Social Engineering in Person

TL;DR: The countermeasure that stopped a live payment-terminal swap was one phone number and permission to use it. Attackers walked into our locations as printer technicians and vendor reps. One arrived with hacked payment terminals, our exact model, ready to install. A simple policy, anyone touching equipment means you call IT first, ended that attempt with the attacker dropping his gear and running.

A note before the stories: I don’t name companies or locations in these articles, and I generalize identifying details. Specifics are a gift to attackers, even decades later, and the discretion is part of the trade. It’s also, not coincidentally, what my ghostwriting clients rely on when they hand me their own war stories.

Social engineering has a physical branch, and at a major national retailer we met it repeatedly.

The classic was the printer guy. A man walks into a location in work clothes, says he’s here to service the laser printers, replace the cartridges, the big bulky units everyone had back then. The person on site doesn’t know any better, and why would they? Printer service visits are real things that really happen.

I have a particular contempt for this kind of attacker, because of who he uses.

He walks past every piece of technology the company paid for and goes straight to the person at the front counter, somebody hired to be helpful, and turns that helpfulness into his way in. When it works, the clerk who opened the door carries the guilt, and I think that’s backwards. The blame belongs to whoever sent that clerk to work without a rule to follow.

Except the printer guy doesn’t want the printers. He wants the building. Once inside, he can look at what is on desks, what’s on screens, what’s plugged into what, and sometimes he can swap equipment while he’s at it. The printer is the pretext; the access is the payload.
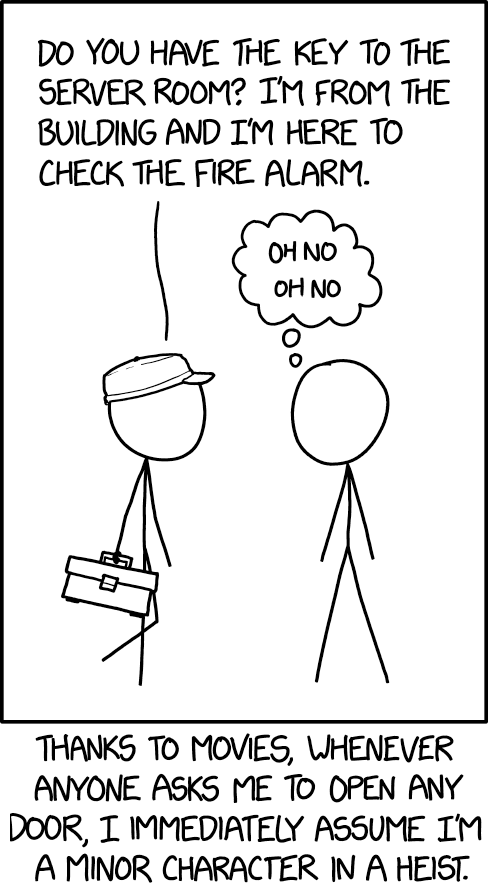
xkcd comic: a man in a cap carrying a toolbox asks for the key to the server room, saying he's from the building and here to check the fire alarm, while the other figure thinks oh no, oh no. Caption: thanks to movies, whenever anyone asks me to open any door, I immediately assume I'm a minor character in a heist.
“Heist” by Randall Munroe, xkcd #2077. Licensed under CC BY-NC 2.5.

How did the fake printer technician try to swap a POS terminal?

The serious version of this attack came for the payment terminals. A man showed up at one of our locations to service the point-of-sale terminals, carrying replacements. Hacked replacements: the same model we ran, modified to intercept cards and capture the card verification data, the security code that makes stolen numbers usable.

Think about what that terminal would have done.

The printer is the pretext; the access is the payload.

Every customer who paid with a card at that register would have handed a stranger a usable card number and security code, and none of them would have known until the fraudulent charges showed up. Those people trusted the store with their money. A skimmer turns that trust into somebody else’s spending money, and the store’s name ends up in the news story.

What stopped him was a policy we’d just rolled out, and its power was its simplicity.

We didn’t train staff to evaluate technicians or inspect equipment; frontline staff can’t be equipment inspectors and shouldn’t have to be. The policy was: anyone shows up wanting to touch equipment, you call IT. Here’s the number. That’s the whole policy.

The staff called. Something in the exchange spooked the man, because he dropped his gear and ran.

We did forensics on what he left behind and confirmed it: a compromised terminal, our exact model, ready to skim every card in the store. We never caught him. We never had to; the attack died at a phone call.

The phone version of the printer guy

The same pretext works by telephone. Callers claiming to be printer vendors would ring locations and ask who was in charge of what: who runs IT, who approves purchases, who’s the manager’s manager. That’s reconnaissance for spear phishing. Map the hierarchy, then craft emails impersonating the right names to the right targets. Those attempts failed with us for the same unglamorous reason: staff had strict instructions not to give out organizational information, full stop.

The person at the front desk who refuses to recite the org chart to a stranger on the phone is doing security work, and I think they deserve to hear that from their bosses. A company that treats that caution as bad customer service, and apologizes to the irritated caller, teaches every employee that being pleasant to strangers outranks protecting coworkers, and attackers count on companies teaching exactly that.

The attack that swaps your payment terminals arrives dressed as a service call. The defense is a phone number and permission to use it.
Share on X

Why does in-person social engineering endure?

Why in-person social engineering still worksDecades of firewalls have not retired the man in the work shirt, and the economics explain why. A physical pretext attack costs a uniform, a clipboard and nerve. It defeats every network control the target owns in one stroke, because it never touches the network, it touches the loading dock. Its failure mode is gentle: a technical intrusion leaves logs, while a challenged impostor simply leaves the building and is gone. Low cost, high yield, graceful abort. Attackers are rational, and the rational move against a well-defended network is frequently the front door. The pretexts evolve with the office equipment, printers then and network gear now, but the play is constant.Why the man in the work shirt still worksLow cost, high yield, graceful abort.1The costA uniform, a clipboard, and nerve2It bypasses everythingIt never touches the networkIt touches the loading dock3It aborts gracefullyA technical intrusion leaves logsA challenged impostor just leaves4So it stays rationalAgainst a well-defended network,the front door is the sensible moveArrive as somebody whose presence requires no explanation, and let normalcy do the work of anexploit.
Why in-person social engineering still worksDecades of firewalls have not retired the man in the work shirt, and the economics explain why. A physical pretext attack costs a uniform, a clipboard and nerve. It defeats every network control the target owns in one stroke, because it never touches the network, it touches the loading dock. Its failure mode is gentle: a technical intrusion leaves logs, while a challenged impostor simply leaves the building and is gone. Low cost, high yield, graceful abort. Attackers are rational, and the rational move against a well-defended network is frequently the front door. The pretexts evolve with the office equipment, printers then and network gear now, but the play is constant.Why the man in the work shirtstill worksLow cost, high yield, graceful abort.1The costA uniform, a clipboard, and nerve2It bypasses everythingIt never touches the networkIt touches the loading dock3It aborts gracefullyA technical intrusion leaves logsA challenged impostor just leaves4So it stays rationalAgainst a well-defended network,the front door is the sensible moveArrive as somebody whose presence requires noexplanation, and let normalcy do the work of anexploit.

Decades of firewalls haven’t retired the man in the work shirt, and the economics explain why. A physical pretext attack costs a uniform, a clipboard, and nerve. It defeats, in one stroke, every network control the target owns, because it doesn’t touch the network; it touches the loading dock. And its failure mode is gentle: a technical intrusion leaves logs, while a challenged impostor leaves a building, as ours did, and is simply gone. Low cost, high yield, graceful abort.

Attackers are rational, and against a well-defended network the rational move is frequently the front door. I think it’s negligent for a company to pour its security budget into the network and leave the front door to whoever happens to be working that shift, with no rule and no phone number.

The pretexts evolve with office equipment, printers then, network gear and access points now, but the play is constant: arrive as someone whose presence requires no explanation, and let normalcy do what an exploit would otherwise have to. The defense is equally constant, and that’s the encouraging half of this story.

Verification procedures don’t rust the way software does. The call-IT policy that stopped our terminal swap would stop the same attack today, unmodified.

My take

Hand every location one phone number and permission to use it. Anyone who shows up to touch equipment, staff call IT first. That rule made an attacker carrying a hacked payment terminal drop his gear and run. Tell staff never to recite the org chart to a caller, and back them when a stranger gets irritated. Front-desk caution is security work. A procedure like that doesn’t rust, and it would stop the same attack today.

How do you design against social engineering?

Both defenses share a shape worth stealing. They don’t ask frontline people to detect deception, a losing game against a professional. They give frontline people a single cheap action that routes the decision to someone equipped to make it. Call this number. Don’t answer that question. The attacker’s craft is defeating judgment; the defense removes judgment from the encounter.

Physical social engineering pretexts and the defense that worked
Attack Pretext Defense
Fake printer technician Servicing the laser printers to gain access to the building Anyone who wants to touch equipment, staff call IT first
Payment terminal swap Servicing point-of-sale terminals, carrying hacked units of our exact model The call-IT policy; the attacker dropped his gear and ran
Phone reconnaissance A printer vendor asking who runs IT and who approves purchases Strict instructions never to give out organizational information

Executives who write about security keep gravitating toward the digital and skipping the man in the work shirt, and I think they’re shortchanging their own readers.

Those readers run warehouses, stores, and offices where he’s the live threat today. If you stopped an impostor at your door, that story belongs in your book, along with the one-line policy that stopped him. A store manager can hand that chapter to the front counter on Monday morning, and it’ll protect more customers than another chapter on firewalls.

For more from this series, see The Cybersecurity Hub: breaches, audits, and hard-won security lessons from 33 years in the trenches.

Frequently Asked Questions

What is physical social engineering?
Deception conducted in person: attackers pose as vendors, technicians, or service staff to gain building access, gather information, or swap equipment. The stated purpose, like printer service, is a pretext for the real objective.
How do POS skimming attacks work?
Attackers replace legitimate payment terminals with modified units of the same model that intercept card data, including the card verification code. Installation requires physical access, so the attack arrives dressed as a service visit.
What policy stops fake vendor attacks?
A single-action rule: anyone requesting access to equipment triggers a call to IT at a posted number. It removes the judgment burden from frontline staff and routes the decision to people who can verify the visit.

About the Author
Richard Lowe, professional ghostwriter

Richard Lowe is a professional ghostwriter and author with 113+ books authored and 54+ ghostwritten. Before writing full time he spent 33 years in enterprise technology, including 20 years as Director of Computer Operations and Technical Services at Trader Joe's. He writes nonfiction, fiction and memoir, and works with executives and experts on books that build authority.

More about Richard Lowe →

Disclaimer

The views and opinions expressed in this blog post are solely those of Richard Lowe and are based on personal experience and research. This content is for informational purposes only and should not be construed as professional legal, financial, accounting, or business advice. Always consult with qualified professionals before making important business or legal decisions. Richard Lowe is not a lawyer, accountant, or licensed professional advisor, and this content does not establish any professional relationship.